Apache Commons Text

漏洞影响:<=1.9.x 起因:看到战队转发了一条Y4tacker师傅的星球文章。 简单跟了一下发现挺简单的一条利用链。 利用链 StringSubstitutor#replace StringSubstitutor#substitute StringSubstitutor#resolveVariable ScriptStringLookup
漏洞影响:<=1.9.x
起因:看到战队转发了一条Y4tacker师傅的星球文章。
简单跟了一下发现挺简单的一条利用链。
利用链
StringSubstitutor#replace
    StringSubstitutor#substitute
        StringSubstitutor#resolveVariable
            ScriptStringLookup#lookup
前置知识
根据名称得到脚本引擎
ScriptEngine engine = new ScriptEngineManager().getEngineByName("JavaScript");
        engine.eval("java.lang.Runtime.getRuntime().exec(\"calc\")");
此方法能弹出计算器。(emmm没去细了解。)
漏洞分析
StringSubstitutor#replace
    StringSubstitutor#substitute
StringSubstitutor#resolveVariable这三段其实跟Log4j是差不多的。目的:为了将${}中间的内容提取出来。
往下走会来到:
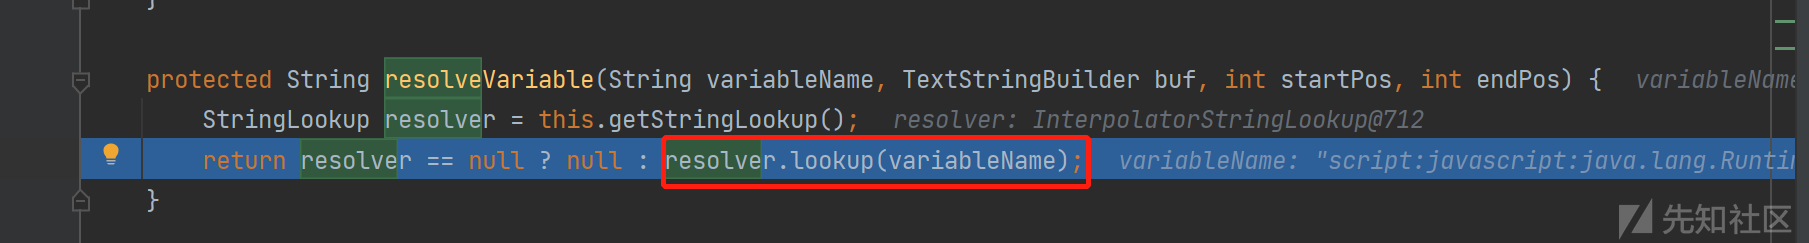
跟进
匹配第一个:前面的字符串然后将余下的字符串另外存入name字符串中,并且会从stringLookupMap中获取对应的lookup,这里即为ScriptStringLookup。


进入ScriptStringLookup#lookup,会根据:分割字符串。最终导致该漏洞触发。

漏洞修复
在InterpolatorStringLookup#lookup中stringLookupMap被缩短了,没有了key=script

删除了dns、url、script。
可以分别来看看。
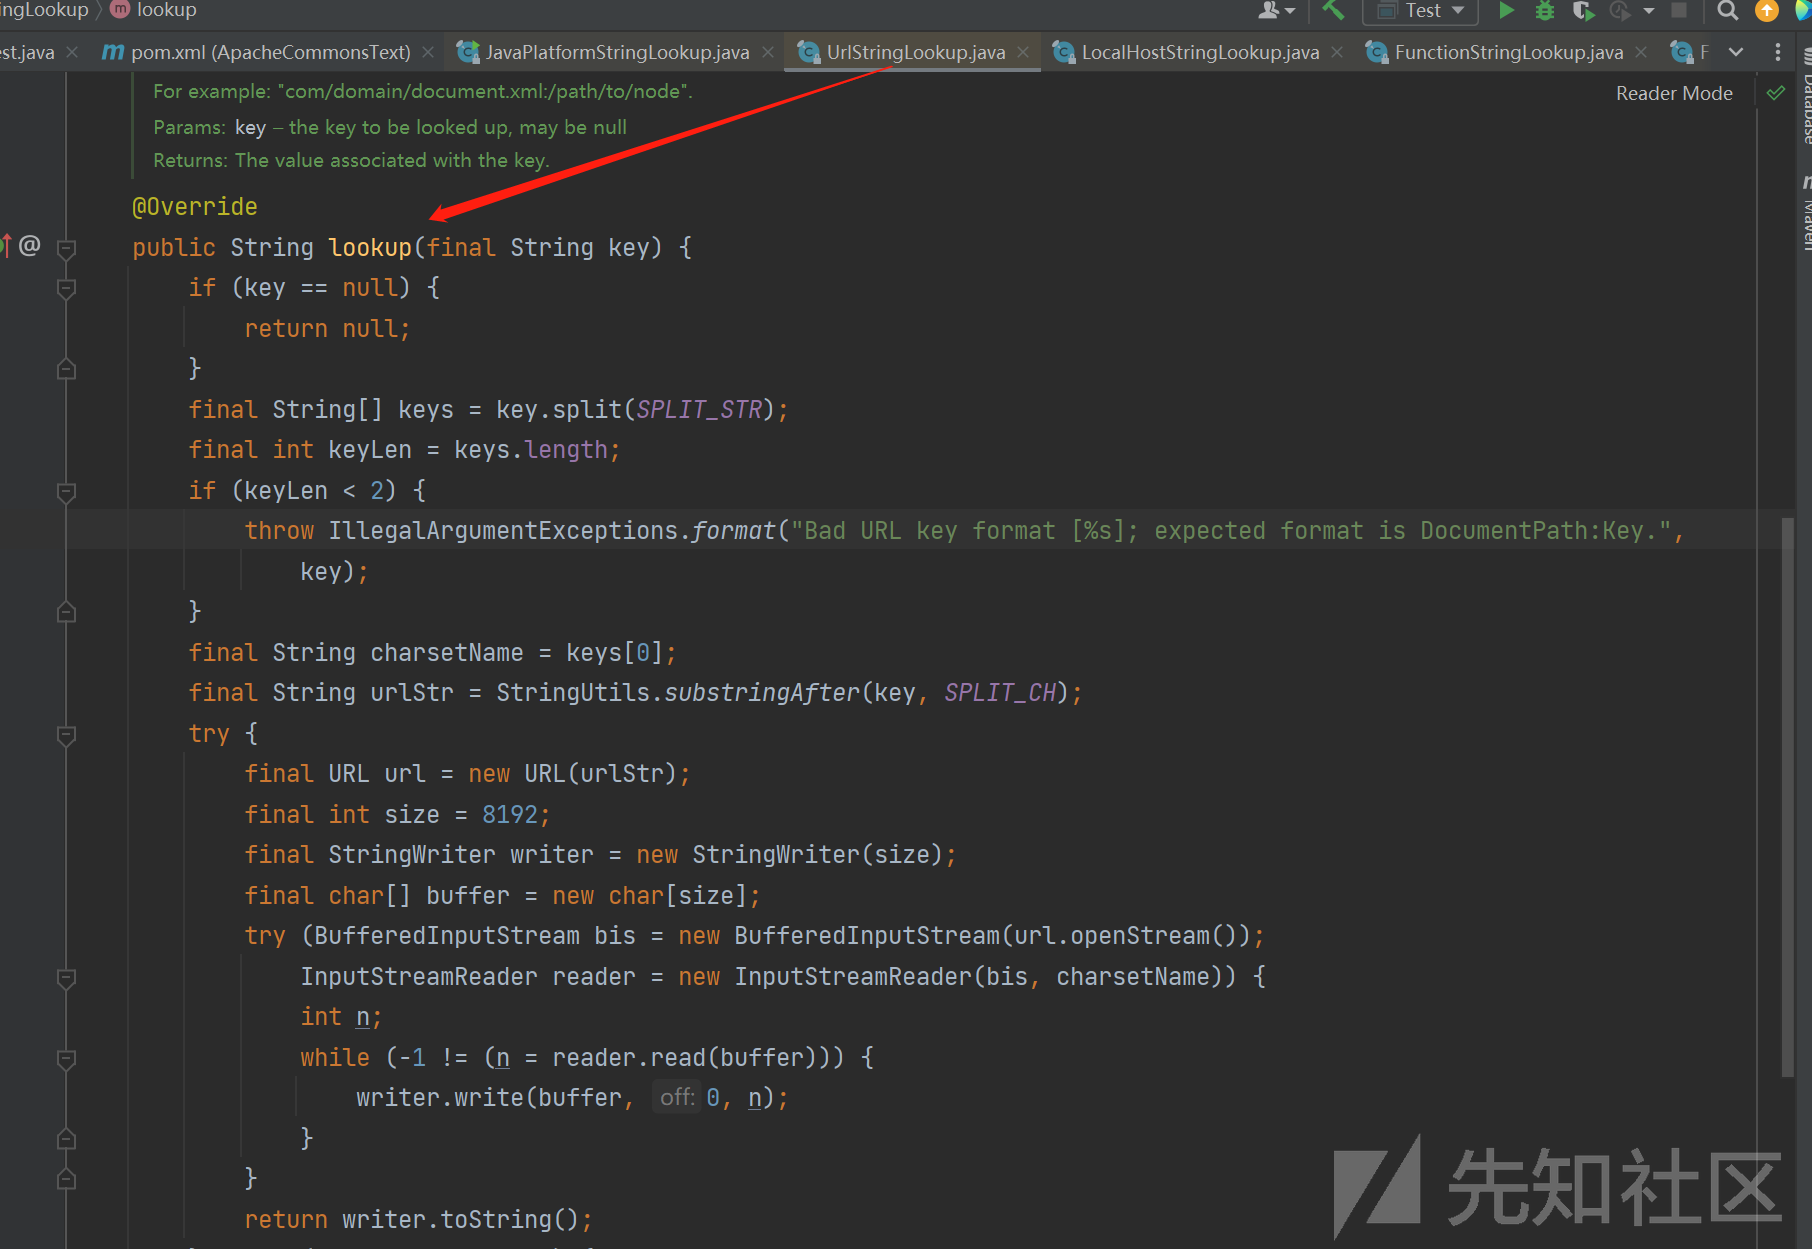
URL
看了代码让我想到了URLClassLoader异常回显(可惜没有实例化)
DNS
主要用于探测吧。
inetAddress.getHostAddress() 获取IP地址
inetAddress.getHostName() 获取主机名
inetAddress.getCanonicalHostName()
getCanonicalHostName方法和getHostName方法一样,也是得到远程主机的域名。但它们有一个区别。getCanonicalHostName得到的是主机名,而getHostName得到的主机别名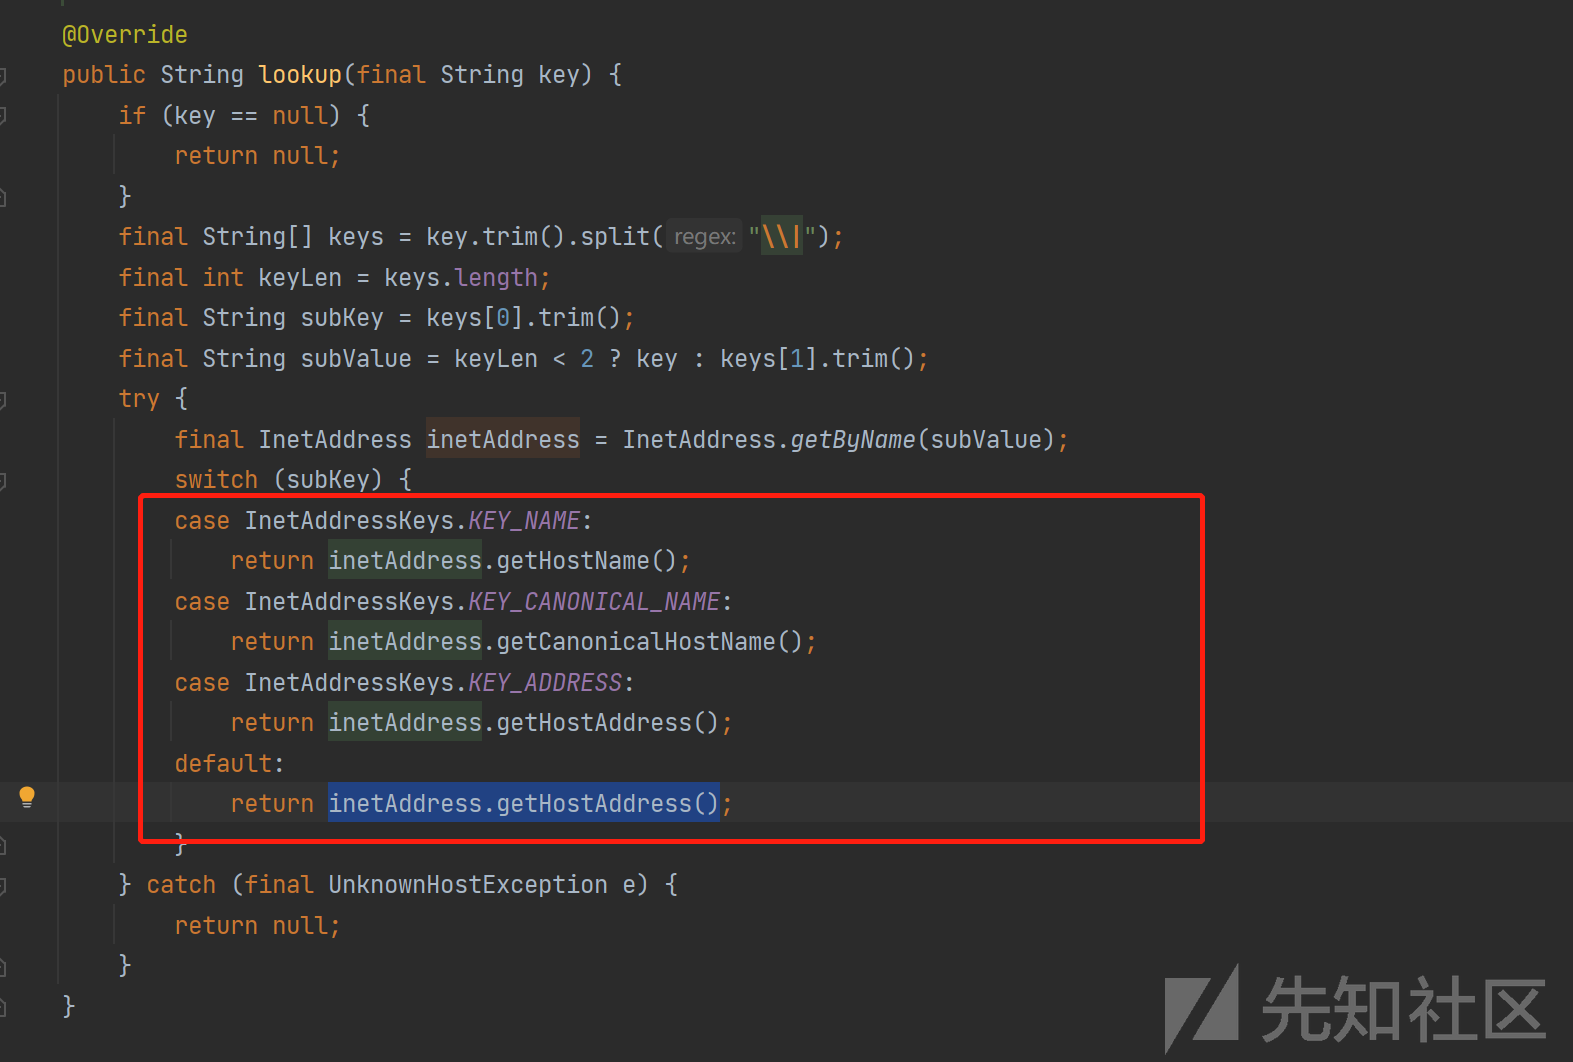

END